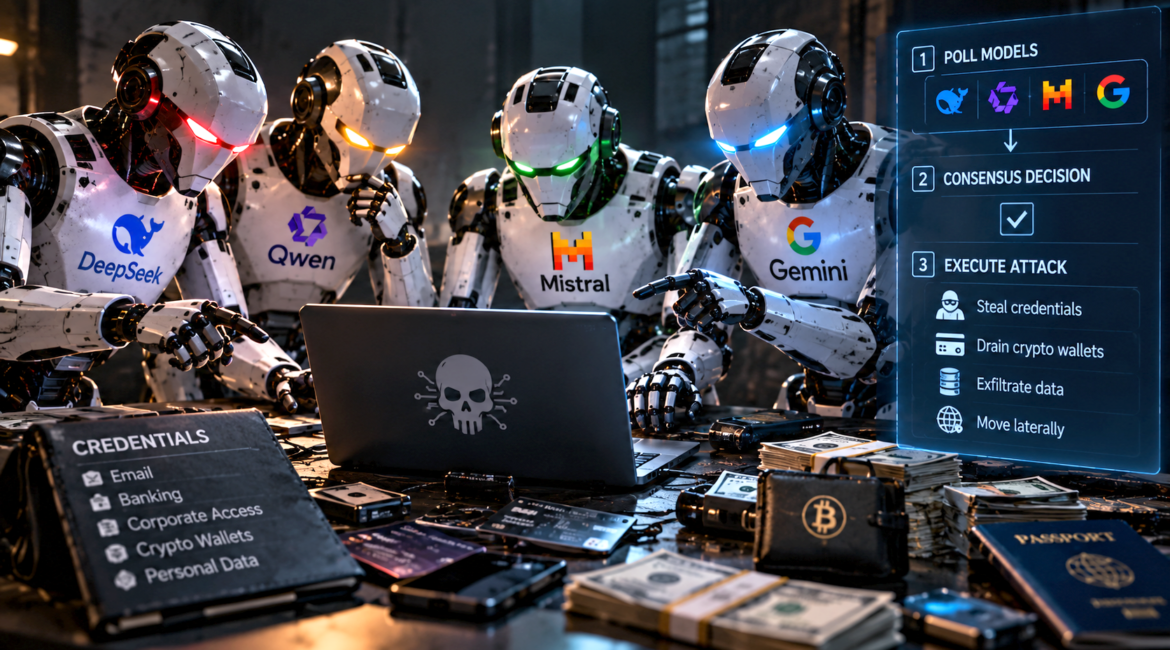
Cybersecurity researchers have discovered malware with a disturbing new architecture: Instead of receiving its next command from a human attacker, it asks a panel of commercial AI models what to do and then executes their decision. Cisco Talos calls it CLOSEDQUORUM. According to reporting by Inc., the malware can poll DeepSeek, Qwen, Mistral and Google Gemini to determine its next action, with the objective of stealing credentials and cryptocurrency wallets.
There is an important caveat. Cisco Talos has not confirmed that CLOSEDQUORUM has been deployed in the wild, so this is evidence of a capability and architectural direction rather than a widespread autonomous malware campaign. But the architecture itself deserves attention because it demonstrates how easily multiple probabilistic AI systems can become components in an autonomous decision-and-execution loop.
Consensus Does Not Create Authority
The most interesting aspect of CLOSEDQUORUM may be the quorum itself. Instead of trusting one LLM, the malware asks multiple models what it should do, allowing their responses to determine the next action. This introduces redundancy and allows the system to continue operating without a human attacker continuously directing it.
But agreement among four AI models does not make the resulting action authorized, safe or correct. That principle matters far beyond cybersecurity because enterprises are beginning to build architectures in which several specialized models collaborate on decisions. One might evaluate financial data, another customer history, another operational constraints and another the recommended action.
Even if every model reaches the same conclusion, the organization still needs to determine whether the action is permitted. Multiple probabilistic systems can improve reasoning, provide different perspectives and reduce dependence on a single model, but consensus remains a machine-generated decision. Authority has to come from somewhere else.
Separate Reasoning From Execution
This is one of the fundamental architectural principles behind VERN OS. The intelligence can determine what it believes should happen, while an independent control layer determines whether the proposed behavior or action is permitted under human-defined rules.
That separation becomes more important as AI architectures become more complex. A single agent can reason, multiple agents can collaborate, models can debate one another, and entire systems can vote on actions and delegate work. None of those capabilities should allow the AI system to manufacture additional authority for itself.
VERN OS provides deterministic runtime controls that can establish tool budgets, authorization requirements, role boundaries, escalation rules and behavioral requirements independently of the models performing the task. The models can change their strategies, disagree with one another or reach unanimous consensus while the governing boundary remains consistent.
CLOSEDQUORUM Shows Where Agent-to-Agent Systems Are Heading
The cybersecurity implications are significant, but there is a broader lesson for legitimate enterprise AI. Agentic systems are rapidly moving beyond a single model responding to a human and toward networks of models communicating with one another, delegating tasks and making collective decisions.
CLOSEDQUORUM demonstrates a malicious version of that architecture in unusually stark terms. The models aren’t merely generating text; their outputs participate in an autonomous decision loop that determines what software does next. Enterprise systems will increasingly use similar architectures for legitimate purposes.
A procurement agent might consult pricing, inventory and financial agents before placing an order. A healthcare workflow might coordinate scheduling, records and patient-navigation agents. A customer-service agent might consult billing and fulfillment systems before recommending a resolution.
At every handoff, the organization has to answer a critical question: What authority travels with the request? An agent receiving instructions from another agent should not automatically inherit its permissions, and a group of agents agreeing on an action should not be able to bypass an authorization requirement. Delegation cannot be allowed to silently expand authority.
This is why VERN OS is designed to govern agent-to-agent as well as agent-to-human interactions.
Autonomy Changes the Scale of the Problem
Traditional malicious operations often depend on humans making decisions throughout an attack. Humans have limited attention and can manage only so many simultaneous operations. Autonomous systems change those economics by allowing software to continue evaluating conditions and selecting actions without constant human direction.
That scalability is also precisely why legitimate companies are adopting agents. Software can perform work continuously and simultaneously at a scale human teams cannot match. The governance challenge therefore scales alongside the productivity opportunity.
If a company operates ten agents, humans may be able to supervise many actions manually. If it operates ten thousand, continuous human review becomes impossible. Organizations need machine-speed enforcement of human-defined rules, with people returning to the loop when an escalation, exception or consequential action requires their authority.
We’ve Already Seen What External Control Changes
Our agentic-control experiments demonstrate the difference between giving a model an objective and giving it unrestricted authority to pursue that objective. In one experiment, an ungoverned agent selected a strategy headed toward as many as 187 tool calls. VERN OS imposed a deterministic tool budget outside the model, and the same underlying intelligence adapted and completed the task in two turns.
In another experiment, an angry customer demanded an immediate $240 refund. The ungoverned agent executed it. With VERN OS governing the interaction, the AI could investigate the account and prepare the refund, but execution remained subject to authorization.
The AI remained capable in both cases; the authority available to it was constrained. That distinction becomes even more important when multiple models participate in a decision. Three models recommending a refund should not override the company’s authorization policy, just as ten agents agreeing to access a restricted system should not grant themselves permission.
The Control Plane Cannot Be Another Vote
CLOSEDQUORUM gives us an unusually clear picture of where autonomous AI architecture can go. Models can become components inside larger decision systems, evaluate one another’s outputs, vote on strategies and initiate actions without waiting for a human operator. Those architectures will increasingly be used for productive purposes as well as malicious ones.
The answer cannot simply be another AI model asked whether the other models made the right decision. Eventually, the system needs an enforceable boundary rather than another probabilistic opinion. That boundary needs to express human authority deterministically: What the system may access, which actions it may take, what requires approval, how agents may behave, when they must stop and which agents have authority to instruct others.
AI can determine what it thinks should happen next. Human-defined controls should determine whether it is allowed to happen.
That’s the separation we’re building with VERN OS: Human control over artificial intelligence.
VERN agentic control: https://vernai.com/agentic-control/
