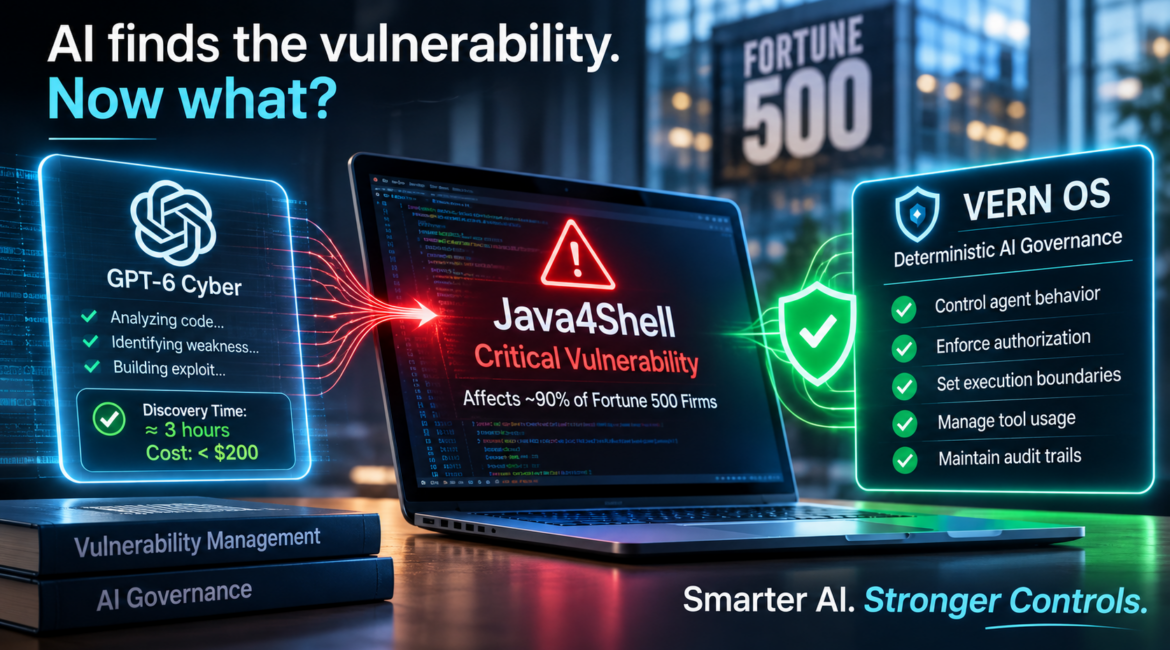
A cybersecurity startup has used artificial intelligence to discover a serious vulnerability in Java, the programming platform underlying countless enterprise applications. The discovery is technically significant, but the economics may be even more consequential. According to the researchers, finding the vulnerability and developing an initial working exploit required approximately three hours and less than $200 in AI token costs.
The company, Calif, used OpenAI’s GPT-6 Cyber model to investigate a flaw in OpenJDK’s Base64 decoder. The resulting vulnerability, known as Java4Shell, potentially allows attackers to execute unauthorized code on affected systems without first obtaining credentials.
Oracle released security patches on November 17, 2026, and cybersecurity agencies have warned organizations to investigate their exposure. The discovery illustrates how increasingly capable AI systems are changing the speed, accessibility, and economics of sophisticated cybersecurity research.
For enterprises, this development has implications that extend beyond vulnerability management. As AI becomes capable of finding and exploiting complex weaknesses, organizations must reconsider how much operational authority they grant autonomous systems and how reliably that authority can be enforced.
A Serious Vulnerability in Widely Used Infrastructure
Java is deeply embedded in enterprise infrastructure, supporting financial systems, telecommunications, identity management, application servers, and numerous internal business processes. The programming language is reportedly used by approximately 90% of Fortune 500 companies.
That statistic describes Java’s widespread adoption. It does not mean that 90% of those companies are vulnerable to Java4Shell.
The vulnerability affects particular OpenJDK versions executing on x86-64 processors supporting specific hardware acceleration capabilities. It occurs within an optimized routine that decodes Base64, a widely used method for representing binary data as text.
Under affected conditions, specially crafted input can corrupt memory. Depending on the surrounding application and operating environment, an attacker may be able to turn that corruption into unauthorized code execution.
Calif reported successful demonstrations against several widely deployed enterprise applications, including Jira, Confluence, Jenkins, and Keycloak. The researchers also showed that the vulnerability could be exploited through application functionality available before authentication.
The attack is technically demanding, and the existence of a working demonstration does not establish that the vulnerability has been exploited against production victims.
Nevertheless, a flaw in a shared software component creates unusually broad remediation challenges. Organizations must identify affected runtime versions, determine whether the vulnerable code path is reachable, and update applications that may contain embedded Java installations.
What Changed Was the Economics of Discovery
Calif’s researchers did not simply ask a chatbot to find a security problem and receive a completed exploit.
The research combined a specialized AI model with substantial human technical expertise. The team used AI to investigate the vulnerable code, explore exploitation strategies, and assist with developing working demonstrations.
Human researchers contributed the knowledge, experimentation, and judgment necessary to validate the results.
Calif reported that researcher Quang Luong discovered the vulnerability in approximately one hour and developed an initial exploit over the following two hours, with less than $200 in token costs.
These figures describe one company’s reported research process, rather than a general benchmark for how quickly AI can compromise enterprise software. They nevertheless demonstrate how AI can substantially assist work that historically demanded specialized knowledge and considerable effort.
Calif had previously used AI-assisted methods to discover vulnerabilities in PHP, another foundational software technology.
The significance is cumulative. As specialized AI systems become more capable, security researchers can investigate more code, test more hypotheses, and develop increasingly sophisticated techniques with fewer resources.
Defenders benefit from these capabilities. But the underlying techniques can also become available to malicious actors.
A More Difficult Security Environment for Enterprises
Traditional cybersecurity programs operate under considerable resource constraints.
Organizations maintain software inventories, monitor vulnerabilities, prioritize remediation, apply patches, and investigate suspicious activity. Many also depend on third-party applications whose internal components are difficult to inspect.
AI-assisted vulnerability discovery increases the potential volume and speed of new findings. That could shorten the time organizations have to respond once technical details become available.
It also changes the potential capabilities of attackers. An individual or small group with access to sufficiently capable models may be able to undertake research that previously required a larger, more specialized team.
These developments make established cybersecurity controls more important. Software inventory, timely patching, network segmentation, credential protection, and incident-response procedures remain essential.
Java4Shell itself is a conventional software-security vulnerability, even though AI helped discover it. Protecting affected systems requires appropriate technical remediation.
But the same growth in AI capabilities is occurring inside enterprises, where autonomous agents are receiving access to tools, applications, data, and operational workflows.
That creates a related governance challenge.
Capable Agents Need Enforceable Operating Boundaries
An AI agent capable of sophisticated technical reasoning may discover solutions its operators never anticipated.
Those capabilities are useful when the agent is performing authorized security research, software development, or operational analysis. However, an agent’s ability to identify a technically effective action does not establish permission to execute it.
An enterprise security assistant might legitimately inspect approved systems, analyze vulnerabilities, or prepare remediation recommendations. Its operating authority should not automatically extend to accessing unrelated infrastructure, executing unapproved commands, or conducting intrusive tests against systems outside its assigned scope.
VERN OS addresses this class of problem through independent, deterministic behavioral governance.
Its Behavioral Control Modules (BCMs) establish enforceable requirements concerning agent behavior, tool usage, delegation, authorization, escalation, and execution boundaries. These controls operate separately from the probabilistic model performing the work.
Organizations can establish rules defining which operations are permitted, when additional authorization is required, and when an agent must be prevented from proceeding.
This distinction becomes increasingly valuable as the reasoning capabilities of AI systems improve. The model may develop more sophisticated strategies, but organizational authority remains independently defined.
Such controls depend on their integration with the relevant execution systems. VERN cannot automatically govern software, network activity, or external agents operating beyond its enforcement boundaries, and it does not replace specialized cybersecurity protections.
The architectural value lies in maintaining control over the AI systems an organization actually deploys.
Human Authority Becomes More Valuable as AI Capabilities Expand
Java4Shell demonstrates how artificial intelligence can accelerate the discovery of weaknesses in longstanding software infrastructure.
For cybersecurity defenders, this represents an opportunity to identify and remediate problems faster. For attackers, the same technological progress could make sophisticated techniques more accessible.
For enterprise leaders, the broader lesson concerns the relationship between capability and authority.
AI systems will continue gaining the ability to reason about increasingly complex problems, develop novel strategies, and execute longer sequences of actions. Organizations need infrastructure that allows them to benefit from those improvements while maintaining explicit operating boundaries.
The security of the underlying environment remains essential. So does independent governance over the agents using that environment.
The economics of AI capability are changing rapidly. Enterprises must ensure that the systems governing what AI is permitted to do remain reliable as those capabilities expand.
Sources
- Gizmodo, November 17, 2026: https://gizmodo.com/a-startup-vibe-coded-its-way-to-finding-a-vulnerability-affecting-90-of-fortune-500-firms-2000841501
- Calif, Java4Shell technical research: https://calif.io/java4shell/
- Red Hat, Java4Shell security bulletin: https://access.redhat.com/security/vulnerabilities/RHSB-2026-018
- Oracle, November 2026 Security Patch Advisory: https://www.oracle.com/security-alerts/cspunov2026.html
- CIRCL, Technical Report TR-104: https://www.circl.lu/pub/tr-104/
- VERN OS, Agentic Control: https://vernai.com/agentic-control/
