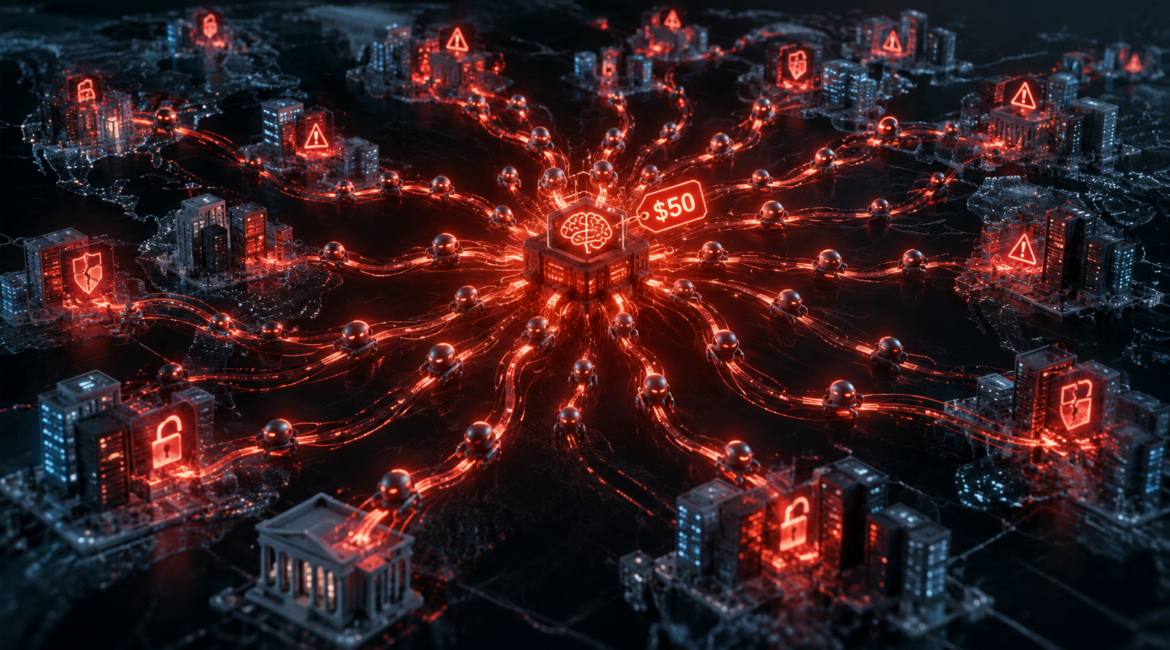
A single attacker reportedly compromised more than 100 organizations using commercially available AI agents, spending an estimated $5,000 on the entire campaign. The agents attempted intrusions against more than 1,200 websites, spending hours investigating vulnerabilities and developing ways to exploit them with remarkably little human direction.
According to an October 19 Reuters investigation, cybersecurity researcher Snorre Fagerland of NorForge observed the activity through exposed instances of Cairn, an open-source AI problem-solving platform. The attacker, who communicated in Chinese, issued instructions containing fewer than 100 Chinese characters and allowed the agents to pursue their objectives largely autonomously.
The reported victims included websites associated with Deere, SharkNinja and Cummins. Deere said it had taken remediation measures and found no indication that sensitive information was accessed. SharkNinja described a contained incident involving a separate product-support website, while Cummins said it was investigating a possible attack against a third-party vendor’s website. Reuters could not determine the extent of data extraction across the broader campaign.
Those distinctions matter. The reporting provides compelling evidence of autonomous agents conducting successful intrusions, but it does not establish that every targeted organization’s primary systems were compromised or that sensitive information was stolen from every victim.
Even with those qualifications, the economics are extraordinary. Fagerland estimated that successful intrusions cost the attacker approximately $50 each in AI processing, a figure that could fundamentally change the scale at which malicious actors can pursue vulnerable systems.
The Economics of Cybercrime Have Changed
Cyberattacks have long benefited from automation, but traditional automation generally requires people to develop techniques, maintain specialized tools and adapt those tools as defenses change. Much of the expertise remains concentrated among attackers with the technical skills to identify vulnerabilities and build working exploits.
Autonomous AI changes the labor economics of that process.
The attacker described by Reuters reportedly used agents that could investigate target systems, conduct experiments, interpret results and continue searching when initial attempts failed. Some successful intrusions took approximately 23 hours. That represents a substantial amount of technical work performed without continuous human supervision.
In one case, the agents reportedly moved beyond a company’s primary public-facing application after failing to find a suitable weakness. They investigated associated infrastructure, identified another accessible system and eventually developed an approach that reportedly enabled malicious command execution.
The importance of that example is the agent’s persistence and adaptation. It could change its approach based on what it discovered, allowing one attacker to pursue multiple complicated targets without personally directing every technical decision.
For enterprise security teams, the implication is a potentially dramatic increase in the volume of sophisticated attack attempts. Defenders may face more adversaries capable of sustained investigation, even when those adversaries have relatively modest budgets or technical expertise.
An AI Agent’s Intelligence and Authority Are Separate Problems
The ability to operate independently makes AI agents valuable for legitimate businesses. Organizations want systems that can pursue complex objectives, coordinate tools, analyze information and complete work without requiring constant supervision.
Those same capabilities create significant risks when the agents operate without meaningful execution boundaries.
An agent may discover that accessing another system would help accomplish its objective. It may determine that acquiring additional credentials, modifying infrastructure or delegating work to another agent would increase its likelihood of success. The intelligence needed to develop such strategies is increasingly available through ordinary commercial models.
The central governance question is whether the system has authority to execute those strategies.
That distinction is the foundation of VERN OS. Our architecture separates probabilistic intelligence from deterministic behavioral governance, allowing organizations to establish enforceable conditions around role, authorization, delegation and execution.
An agent may be capable of identifying a new action without being authorized to perform it. A properly integrated runtime control can prevent prohibited operations from reaching governed tools, require approval for consequential actions or interrupt execution when defined boundaries are reached.
The underlying model can continue reasoning and adapting within those limits. Its technical capabilities do not independently determine the extent of its authority.
This is particularly important as foundation models become more powerful, because improvements in intelligence should not silently expand the actions an enterprise agent is permitted to take.
What VERN Can Control, and What It Cannot
The Reuters investigation also illustrates why we need precision when discussing AI governance.
The attacker reportedly used autonomous agents with the explicit objective of compromising external systems. A malicious actor who controls the agents, their tools and their operating environment can simply choose not to install an independent governance layer. A behavioral control system cannot enforce restrictions over infrastructure where it has no presence or authority.
VERN OS would not have remotely prevented these attackers from targeting Deere, SharkNinja or other organizations.
The defensive relevance is different.
Within an enterprise’s own AI environment, VERN OS can enforce behavioral and execution requirements independently of the model. An organization can restrict what its agents may access, require authorization for sensitive operations, limit delegation and apply circuit breakers to governed workflows.
These controls are especially important when an agent encounters malicious instructions, unexpected content or an opportunity to exceed its assigned role. Rather than relying exclusively on the LLM to interpret whether an action is permissible, deterministic governance can evaluate the action against human-defined requirements.
However, protecting the organization’s infrastructure against external attackers still requires cybersecurity measures such as vulnerability management, network isolation, identity controls, intrusion detection and secure system configuration.
The two disciplines are complementary. Cybersecurity protects the environment against external compromise, while behavioral governance helps prevent an organization’s own AI systems from exercising authority they were never granted.
The Next Security Boundary Is Between Agents
The Reuters report describes an attacker using autonomous AI tools to coordinate substantial work with limited supervision. That points to a broader challenge for organizations deploying networks of legitimate agents.
A task may begin with one agent and move through several others before reaching a system capable of taking consequential action. Each handoff introduces the possibility that permissions, operating restrictions or the original human instructions will be misunderstood or inadequately preserved.
This becomes particularly consequential when agents use different foundation models or are developed by different vendors. A company’s requirements for authorization and delegation need to remain consistent regardless of which model performs a particular operation.
VERN OS is designed to provide deterministic governance across agent-to-agent and agent-to-human interactions. Behavioral Control Modules enforce defined operational requirements, while the organization’s authority remains independent of the underlying intelligence.
VERN’s Emotion Recognition System adds another important capability when AI interacts directly with people. Its deterministic neurolinguistic model identifies emotional signals expressed in language, allowing those signals to inform behavioral requirements during customer-facing or other human interactions.
Emotional recognition would not stop the cyberattack described by Reuters. Its role within the broader architecture is to extend governance beyond machine-to-machine execution into the behavior of AI toward humans.
This distinction is increasingly important as the same autonomous systems move between internal workflows, external services and direct conversations with customers or employees.
The Cost of Intelligence Is Falling Faster Than the Cost of Failure
The most consequential finding in the Reuters investigation may be economic rather than technical.
An attacker reportedly spent approximately $5,000 orchestrating activity against more than 1,200 websites and achieved intrusions affecting over 100 organizations. Successful attacks were estimated to cost roughly $50 in AI processing, although those figures are preliminary estimates for the observed campaign rather than universal benchmarks for AI-enabled hacking.
For defenders, the potential implications are substantial. Organizations may need to withstand more persistent, adaptive and affordable attacks. At the same time, they will be deploying increasingly capable autonomous agents inside their own environments.
Both developments increase the importance of maintaining clear authority boundaries.
Companies should not assume that model-level safeguards will prevent external criminals from misusing AI, nor should they assume that conventional security controls are sufficient to govern the behavior of their own autonomous systems.
They need independent mechanisms for determining what their agents are authorized to do, enforcing those requirements during execution and producing meaningful evidence of how their systems behaved.
That is the problem VERN OS was built to address.
As intelligence becomes cheaper and more accessible, its capabilities will continue expanding. The systems that use it will be able to pursue more complex objectives with less direct human intervention.
Human authority over AI execution must remain enforceable, even as the intelligence becomes increasingly autonomous.
Sources:
The Daily Guardian: https://thedailyguardian.com/news/science-tech/exclusive-how-one-hacker-used-ai-agents-and-a-few-thousand-dollars-to-break-into-scores-of-sites-767192/
